BYOD says it hacked UNM. We don’t know if that’s true, and UNM hasn’t confirmed it. Here’s what we know about the gang.
Who BYOD is
BYOD is new. WatchGuard, a security company, says it was first seen in September 2026. WatchGuard says its leak site “looks exactly like” one run by another new group, UmBra.
A leak site is where a gang posts the names of those it says it hit. I read BYOD’s on Monday night. We don’t link it.
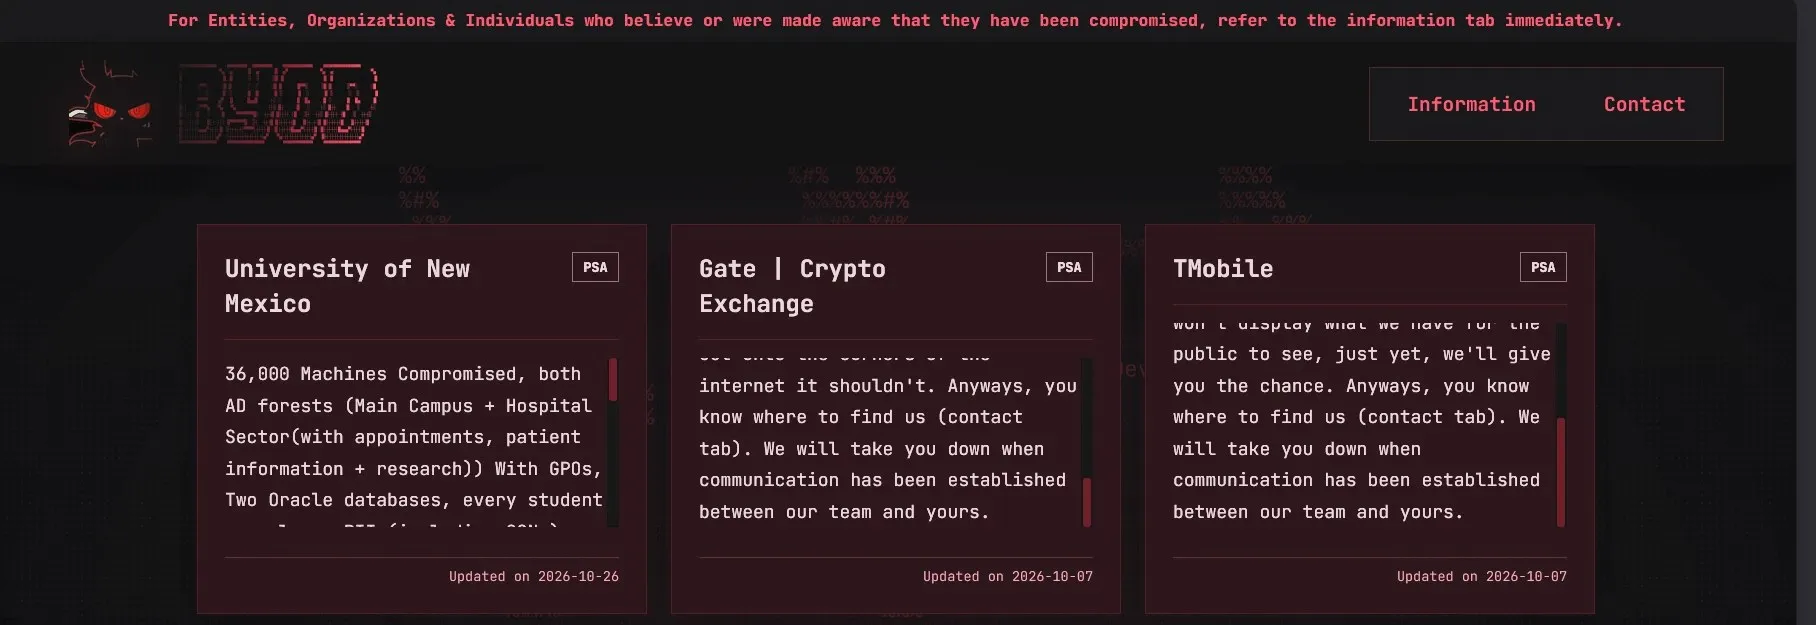
Who else it lists
Before UNM, ransomware.live lists eight BYOD victims, all companies. They include Trump Mobile, T-Mobile and Gate, a crypto exchange. None is a hospital or a school.
Trump Mobile is the best known. The Register says BYOD leaked data on 3,615 Trump Mobile customers. BYOD says it got in through a password-stealing program on a partner company worker’s computer. That is its word only.
On Monday night, its own site showed only six of the nine. Three earlier listings were gone. The site doesn’t say why.
What it wants
Money. Its site’s question page says, “The motive is to be paid.” It takes Bitcoin or Monero only. It tells victims not to go to the police. It also says it wants to “expose the vulnerabilities,” then adds, “We also like the money of course.”
WatchGuard says BYOD steals data and threatens to post it.
What it says about UNM
BYOD’s listing says it has 36,000 UNM computers and “every student + employee PII (including SSNs).” We can’t check it. As of Monday night, the listing shows UNM’s name but no data.
UNM calls the problem a “cybersecurity issue” and hasn’t named a group. In its 6:08 p.m. update, UNM said systems began coming back at 2:30 p.m.
How it has played out before
BYOD’s past posts follow the same steps.
- It breaks in and tells the victim.
- If the victim doesn’t deal, it posts the name with a warning. T-Mobile’s says, “We won’t display what we have for the public to see, just yet, we’ll give you the chance.”
- If the victim still won’t deal, the data goes public. BYOD says Trump Mobile told it, “We have no team to handle this.” Then it put out data on 3,615 Trump Mobile customers. It says another company, Eteam, “just ignored us.”
- Its site says a victim who pays gets its data deleted and its name kept off. We found no report that any victim paid.
UNM is at step 2. Its listing shows a name and a warning, but no data.
Not yet known
- If BYOD is behind what is happening at UNM.
- If any student, employee or patient data was taken.
Read more
- BYOD’s UNM listing on ransomware.live.
- Our main story on the outage.
Reader comments
What do you think?
Burqueños know this city best. Add what you've seen, ask a question, or push back on the story.
Loading comments…
New here? Sign up with your email. Confirm it and you're in, no password.
Comments are closed on this story.
Comments are the commenter's own words, not the Ledger's. Comment rules